Summary: Traffic flood protection keeps networks, applications, and APIs available when request volumes exceed what they can process. Radware is best for hybrid on-premises and cloud defense, Akamai Prolexic fits large-scale network scrubbing, Cloudflare covers edge-based web and API protection, and AWS Shield fits workloads already running on AWS.
What is a Traffic Flood?
A traffic flood occurs when a system receives more network requests or data than it can process efficiently. The excess traffic can consume bandwidth, connections, memory, CPU, or application resources. As capacity is exhausted, legitimate requests may become slow or fail completely.
Traffic floods can target different layers of a system. Some overwhelm network infrastructure with packets, while others send large numbers of HTTP requests to web servers, APIs, or specific application endpoints. A flood may be malicious, but unexpected legitimate traffic can produce similar effects.
DDoS Solutions for Traffic Flood Prevention: At a Glance
The table below summarizes the main differences between the solutions covered in this section, including where each one fits and what to watch out for. Each solution is explored in more detail underneath.
| Category |
ソリューション |
Best For |
Key Strengths |
Things to Consider |
| Dedicated DDoS Mitigation Platforms |
ラドウェアのDDoS防御 |
Hybrid flood defense across on-prem, cloud, and mixed environments |
Behavioral detection, 30 Tbps scrubbing, flexible deployment modes |
Dashboards and report retention offer limited customization |
| Dedicated DDoS Mitigation Platforms |
Akamai Prolexic |
Large-scale network flood scrubbing with a managed SOCC |
32 scrubbing centers, 20+ Tbps capacity, zero-second SLA |
Cost and limited visibility into vendor-run mitigation |
| Dedicated DDoS Mitigation Platforms |
NETSCOUT Arbor DDoS Protection |
Service providers and large networks needing layered defense |
On-prem, cloud, and virtual options with ATLAS intelligence |
Deployment and tuning require specialized in-house skills |
| Dedicated DDoS Mitigation Platforms |
Imperva DDoS Protection |
Web, network, and single-IP flood protection with fast SLAs |
3-second L3/4 SLA, 13 Tbps scrubbing, ISP-agnostic routing |
Defaults and SIEM logging need review before production use |
| Edge and Cloud Platform Flood Protection |
Cloudflare DDoS Protection |
Web apps, APIs, and networks needing large absorption capacity |
500 Tbps capacity, Spectrum and Magic Transit, 24/7 hotline |
Advanced controls sit on higher tiers and take tuning |
| Edge and Cloud Platform Flood Protection |
Fastly DDoS Protection |
Application and API flood mitigation without manual tuning |
Adaptive Threat Engine, edge mitigation, no attack-traffic fees |
Advanced configuration and support responsiveness draw complaints |
| Edge and Cloud Platform Flood Protection |
AWS Shield |
Protecting internet-facing workloads hosted on AWS |
Inline L3/4/7 mitigation, traffic baselining, response team |
Key diagnostics and cost protection need the Advanced tier |
| Edge and Cloud Platform Flood Protection |
Azure DDoS Protection |
Azure virtual networks needing always-on network-layer defense |
Adaptive tuning, edge scrubbing, 15-minute rapid response SLA |
Layer 7 needs a separate WAF, and pricing is often flagged |
What Causes Traffic Floods?
DDoS攻撃
A distributed denial-of-service (DDoS) attack floods a target with traffic from many systems at the same time. Distributing requests across multiple source IP addresses makes the traffic harder to block than a flood originating from a single host.
DDoS attacks can exhaust network bandwidth, connection tables, or application resources. For example, an attacker may send large volumes of UDP packets, repeatedly create TCP connections, or request resource-intensive web pages. The goal is to reduce availability for legitimate users.
Botnets and Automated Requests
Botnets are groups of compromised devices controlled by an attacker. They can include servers, computers, routers, and Internet of Things devices. An attacker can instruct thousands of these devices to send requests simultaneously, producing a large traffic flood.
Automated traffic can also come from crawlers, scrapers, vulnerability scanners, and poorly configured scripts. These requests are not always intended to cause an outage, but high request rates can still overload a service. Rate limiting and bot detection can help separate expected automation from abusive traffic.
API乱用
API abuse occurs when clients send requests in ways that consume excessive application resources or exceed intended usage patterns. Examples include repeatedly querying expensive endpoints, submitting large payloads, making requests at very high rates, or creating many concurrent connections.
Unlike simple network floods, API abuse can cause problems with relatively modest traffic volumes. A single API request may trigger database queries, external service calls, or CPU-intensive processing. Authentication controls, request quotas, rate limits, payload limits, and per-endpoint monitoring can reduce this risk.
What are the Risks of Traffic Flooding?
Traffic flooding can affect availability, performance, and infrastructure costs. The impact depends on the traffic volume, target, and resources consumed.
- Service outages: Excess traffic can exhaust bandwidth, CPU, memory, connection pools, or other resources, making services unavailable.
- Higher latency: Systems may continue operating but respond slowly as servers and network devices approach capacity.
- Resource exhaustion: Floods can consume database connections, worker processes, API quotas, and other limited resources.
- Increased costs: Autoscaling, bandwidth usage, logging, and third-party API calls can increase infrastructure expenses during a flood.
- Reduced access for legitimate users: Malicious or automated requests can compete with normal traffic, causing timeouts and failed requests.
- Secondary system failures: Overloaded components can put additional pressure on databases, caches, queues, and dependent services.
Common Types of Flooding Attacks
SYN Floods
A SYN flood exploits the TCP connection process. The attacker sends large numbers of SYN packets to start connections but does not complete the TCP handshake. The target keeps these half-open connections in its connection table while waiting for responses.
As the connection table fills, the server may be unable to accept legitimate connections. Attackers can also spoof source IP addresses, making filtering more difficult. Common defenses include SYN cookies, connection timeouts, rate limiting, and upstream traffic filtering.
UDP Floods
A UDP flood sends large volumes of UDP packets to ports on a target system. Because UDP does not require a connection handshake, attackers can generate packets quickly and may spoof their source addresses.
The traffic can consume network bandwidth and force the target to process unwanted packets. When packets reach closed ports, the system may also generate ICMP responses, adding processing overhead. Rate limiting, firewall rules, and upstream filtering can help control UDP floods.
HTTP Floods
An HTTP flood sends large numbers of HTTP requests to a web application or API. Requests may target pages, search functions, login endpoints, or other operations that require significant server-side processing.
HTTP floods operate at the application layer, so individual requests can resemble legitimate user traffic. Defenses typically combine rate limiting, caching, bot detection, web application firewall rules, and controls that limit expensive requests.
ICMP Floods
An ICMP flood overwhelms a target with large numbers of Internet Control Message Protocol packets, often ICMP echo requests used by the ping utility. Processing and responding to these packets can consume network bandwidth and system resources.
Large floods can reduce the bandwidth available to legitimate traffic or increase load on network devices. Defenses include limiting ICMP traffic, filtering unnecessary ICMP message types, and using upstream mitigation when attack traffic exceeds local network capacity.
DNS Amplification Attacks
A DNS amplification attack uses publicly accessible DNS servers to send large responses to a victim. The attacker sends small DNS queries with the victim's spoofed IP address as the source, causing DNS servers to direct their responses to the victim.
Because DNS responses can be much larger than the original queries, attackers can amplify their available bandwidth. Defenses include preventing IP address spoofing, restricting open DNS resolvers, applying response rate limiting, and using DDoS mitigation services to filter amplified traffic.
Notable Traffic Flood Prevention Solutions
How we selected these solutions: We shortlisted traffic flood prevention solutions based on their ability to detect and filter volumetric network floods, protocol floods, and application-layer request floods, the scrubbing capacity and deployment models they offer, and the automation and support available during an active attack.
Dedicated DDoS Mitigation Platforms
1. Radware DDoS Protection Solutions
Best for: Hybrid flood defense across on-prem, cloud, and mixed environments
Strengths: Behavioral detection, 30 Tbps scrubbing, flexible deployment modes
Things to consider: Dashboards and report retention offer limited customization
Radware DDoS Protection solutions provide DDoS protection for on-premises infrastructure, private and public clouds, and hybrid environments. Detection is based on behavioral algorithms that build a picture of normal traffic and identify deviations, which allows the platform to act on attack patterns it has not seen before rather than relying only on known signatures.
The portfolio spans network-layer (L3/4) and application-layer (L7) flooding, including burst attacks, DNS attacks, encrypted attacks, IoT botnet traffic, and ransom DDoS campaigns. Deployment options include on-demand and always-on cloud services, physical or virtual appliances, and hybrid combinations tailored to a given architecture.
Key features include:
- Behavioral zero-day detection: Algorithms profile traffic behavior to identify new and unknown flood attacks, rather than matching against a fixed signature list.
- Global scrubbing network: The Cloud DDoS Protection Service runs across 25 scrubbing centers with 30 Tbps of mitigation capacity, connected in full mesh mode with Anycast-based routing to reduce latency.
- Multiple deployment models: Cloud services in on-demand or always-on mode, physical or virtual appliances, and hybrid designs that combine both.
- DefensePro X appliance: An on-premises product for automated protection against fast-moving, high-volume, encrypted, or very-short-duration flood traffic.
- DNS flood protection: A dedicated DNS DDoS product that uses behavioral detection and automatic real-time signatures to block DNS-targeted attacks.
- Web DDoS protection: A cloud service aimed at large, dynamic application-layer flood campaigns, filtering attack requests without blocking legitimate traffic.
- Emergency Response Team: A 120-person team acting as the contact point for alerts, strategy, and hands-on support during an attack, with fully managed service options.
- Mitigation SLA: Commitments covering detection time, mitigation time, and service uptime.
Limitations (critical feedback from otherwise positive reviews on G2):
- Dashboard customization: Reviewers note that dashboards and reports follow a standard layout, and would prefer to surface their own key metrics during time-sensitive investigations.
- Reporting retention: Some users mention that attack and traffic data is held on the dashboard for a limited number of days.
- Onboarding effort: A few reviewers describe the initial setup and onboarding as lengthy, with a learning curve for teams new to this type of solution.
2. Akamai Prolexic
Best for: Large-scale network flood scrubbing with a managed SOCC
Strengths: 32 scrubbing centers, 20+ Tbps capacity, zero-second SLA
Things to consider: Cost and limited visibility into vendor-run mitigation
Akamai Prolexic routes inbound traffic through Akamai infrastructure, inspects it, applies mitigation controls, and forwards only filtered traffic to the customer origin. It is available as a cloud service, as an on-premises solution powered by Corero, or as a hybrid of the two, and can run always-on or be activated on demand during an attack.
The service is aimed at enterprises, network service providers, and cloud, hosting, and SaaS platforms. Alongside flood mitigation, Prolexic Network Cloud Firewall sits at the network edge and applies access control lists ahead of a customer's own firewalls.
Key features include:
- Anycast scrubbing capacity: 32 global scrubbing centers with more than 20 Tbps of dedicated DDoS defense capacity, on a network with over 1 Pbps of total capacity, using anycast routing to mitigate near the attack source.
- Proactive mitigation controls: Predefined controls stop more than 98% of attacks instantly, backed by a zero-second mitigation SLA and a 100% platform availability SLA.
- Flexible deployment: In-cloud, on-premises via Corero, or hybrid, so scrubbing can run in-house and fail over to cloud capacity when links risk being saturated.
- Network cloud firewall: Geographic and IP-based access control lists that can be defined by the customer or suggested by Prolexic, managed centrally and integrated through APIs.
- Connectivity options: Routed GRE requires an advertisable /24 IPv4 or /48 IPv6 block and BGP support, while IP Protect covers smaller or fragmented IP space via anycast routing.
- Direct Connect on-ramp: A private interconnect supporting 10G and 100G ports, delivering GRE traffic up to 1,500 byte packets without MSS adjustment.
- Dual-stack mitigation: Dynamic controls that scale capacity across both IPv4 and IPv6 traffic flows.
- 24/7 SOCC: More than 225 frontline responders across six locations, covering pre-attack preparation, live mitigation, and post-event analysis.
Limitations (critical feedback from otherwise positive reviews on G2):
- Subscription cost: Several reviewers describe the monthly subscription as high relative to alternatives.
- Limited operator control: Users report that most decisions are made by the Akamai SOC, with limited visibility into how mitigation is applied and little insight into the underlying platform.
- Logging depth: Reviewers note that logging is minimal given traffic volumes, and that log generation could be more automated.
- False positives: Some users would like more accurate filtering so that reported incidents reflect genuine attack traffic.
- Automation gaps: A few reviewers mention missing automated mitigations and the absence of automatic throttling, with some initial human intervention still required.
3. NETSCOUT Arbor DDoS Protection

Best for: Service providers and large networks needing layered defense
Strengths: On-prem, cloud, and virtual options with ATLAS intelligence
Things to consider: Deployment and tuning require specialized in-house skills
NETSCOUT's Arbor product line has been used for DDoS defense for more than 25 years and has visibility into 800 Tbps of traffic across more than 550 customers. The approach combines network-wide visibility, automated detection of multi-vector attacks, and orchestrated mitigation that selects where and how attack traffic is filtered.
The line covers both service provider networks and enterprise perimeters. Products can be deployed as managed services, in-cloud, on-premises, or as virtualized instances, and are designed to work together so that detection in one component drives mitigation in another.
Key features include:
- Arbor Edge Defense: An inline appliance placed at the network perimeter between the internet router and the firewall, providing stateless on-premises flood mitigation that does not depend on connection state tables.
- Arbor Threat Mitigation System: Filters malicious traffic at scale while allowing legitimate traffic through, acting as the mitigation layer for large volumetric floods.
- Arbor Sightline: Network-wide visibility and detection for service providers and complex enterprise networks, with a Sentinel option that automates response to simplify incident handling.
- Arbor Cloud: A fully managed cloud service built on 16 global scrubbing centers with more than 15 Tbps of mitigation capacity.
- ATLAS threat intelligence: A global feed of DDoS activity across more than 200 countries and 375 industry verticals, used to update countermeasures on the mitigation products.
- Orchestrated mitigation: Multiple mitigation methods are coordinated automatically, with AI used to select the approach applied to a given attack.
- Arbor Insight: Traffic engineering and analytics that extend the data available in Sightline workflows.
- Deployment flexibility: A mix of managed services, in-cloud, on-premises, and virtualized options.
Limitations (as reported by users on G2):
- Deployment complexity: Reviewers describe initial setup and configuration as complex, requiring specialized expertise and skilled teams for day-to-day management.
- Cost: Pricing is raised repeatedly as a concern, with several users saying it puts the platform out of reach for smaller organizations.
- Documentation: Users report that documentation and administrator guidance are areas that need improvement, including API documentation and filtering options.
- Scrubbing capacity planning: Some reviewers note that effectiveness depends on provisioning sufficient scrubbing capacity, and that appliances with higher throughput may be needed for large volumetric attacks.
- Detection gaps: A small number of users report false positives and say some newer attack types are not detected, with requests for a broader signature set.
- Ongoing effort: Reviewers mention recurring learning cycles and licensing structures that are difficult to interpret.
4. Imperva DDoS Protection
Best for: Web, network, and single-IP flood protection with fast SLAs
Strengths: 3-second L3/4 SLA, 13 Tbps scrubbing, ISP-agnostic routing
Things to consider: Defaults and SIEM logging need review before production use
Imperva DDoS Protection is a cloud service covering volumetric, protocol-based, and Layer 7 attacks. It is packaged as three options that map to different asset types: website protection, network protection, and individual IP protection, so organizations can apply it to web applications, whole infrastructures, or single non-HTTP services.
Mitigation is fully automated and does not require manual activation. The service is ISP-agnostic, works alongside Imperva's cloud web application firewall, and integrates with SIEM systems so DDoS events can be correlated with other security data.
Key features include:
- Layer 3 and 4 mitigation SLA: A guaranteed SLA of three seconds or less for network and protocol floods, with typical mitigation reported within one second.
- Website protection via DNS change: Routing HTTP/S traffic through the Imperva proxy masks the origin server IP and filters flood traffic, with no CAPTCHA step for legitimate requests.
- Network protection deployment options: GRE tunnels, cross connects, and virtual cross connects such as Equinix Fabric Cloud Exchange, in always-on or on-demand mode with flow-based monitoring and automatic or manual switchover.
- Individual IP protection: An Imperva IP is provided as an alternative destination for a protected server, routing all ingress and egress traffic for that IP through the Imperva network. This suits non-HTTP assets or assets that cannot be inspected by a cloud WAF.
- Broad attack coverage: Mitigates UDP floods, SYN floods, DNS amplification, HTTP(S) GET and POST request floods, and Slowloris attacks.
- Scrubbing capacity and routing: 13 Tbps of global scrubbing capacity with high-capacity packet processing, anycast routing, and real-time capacity management across points of presence.
- Adaptive Layer 7 thresholds: Machine learning analyzes traffic patterns and sets thresholds automatically, using heuristic, behavioral, and contextual analysis plus crowdsourced data, with 0.01% of visitors seeing a CAPTCHA challenge.
- Alerting and integration: Attack notifications via email, SMS, and mobile app, with SIEM integration for event correlation.
Limitations (as reported by users on G2):
- Default configuration: One reviewer reports that default settings can allow protection to be bypassed unless the configuration is reviewed before going into production.
- SIEM logging: Users describe audit logging to SIEM as difficult to configure, with concerns about how data is exposed.
- Performance and configuration: Some reviewers mention slow performance across modules and configuration that is not straightforward.
- Signature updates: A reviewer notes that newly published zero-day issues sometimes come with manual remediation suggestions rather than updated signatures.
- Cost: Pricing is raised by multiple reviewers, along with limited room for cost optimization.
- Integration scope: One user reports difficulty integrating the service with a local management system.
Edge and Cloud Platform Flood Protection
5. Cloudflare DDoS Protection
Best for: Web apps, APIs, and networks needing large absorption capacity
Strengths: 500 Tbps capacity, Spectrum and Magic Transit, 24/7 hotline
Things to consider: Advanced controls sit on higher tiers and take tuning
Cloudflare absorbs flood traffic across a global network with 500 Tbps of capacity, which it describes as 23 times larger than the biggest DDoS attack recorded. Protection is delivered from the same network that sits in front of roughly 20% of the internet, so mitigation happens at the edge rather than at a separate set of scrubbing sites.
Coverage extends beyond websites. Cloudflare Spectrum handles TCP and UDP applications, including custom protocols, and Magic Transit protects networks and data centers against Layer 3 and 4 attacks, so the same platform can cover HTTP endpoints and raw infrastructure.
Key features include:
- Network absorption capacity: 500 Tbps of capacity used to soak up large volumetric floods without degrading performance for legitimate users.
- Website and web application protection: Filters flood traffic aimed at sites and applications while keeping them reachable during large attacks.
- Spectrum for TCP and UDP: Extends DDoS protection to applications built on any protocol, including custom ones, covering services running on a server, container, or virtual machine.
- Magic Transit: Protects networks, data centers, and infrastructure against Layer 3 and 4 flood traffic.
- Rate limiting: A separate abuse-prevention control that restricts request rates against specific endpoints.
- Web application firewall and bot management: Adjacent products on the same platform that address application-layer request floods and automated traffic.
- Under Attack support: A 24/7 hotline plus email and phone support for organizations that need help during an active attack.
- Onboarding: Protection is enabled without a lengthy configuration process.
Limitations (as reported by users on G2, covering the wider Cloudflare application security platform):
- Feature tiering: Reviewers repeatedly note that advanced capabilities such as bot management, custom rate limiting, and raw log streaming require higher-priced or enterprise plans.
- Configuration complexity: Users describe overlapping rule layers and a dashboard with many settings, making it unclear which layer owns a given policy.
- False positives: Several reviewers report that managed WAF and bot rules can block legitimate traffic or trap real users in CAPTCHA loops, and that identifying which rule fired means digging through logs.
- Support responsiveness: Users on lower tiers describe slow support response times and reliance on community documentation.
- Origin bypass risk: One reviewer notes that protection only applies to traffic routed through Cloudflare, so an exposed origin IP can be attacked directly unless authenticated origin pulls or firewall rules are enforced.
- Learning curve: Reviewers mention a steep learning curve for teams without dedicated networking or security experience.
6. Fastly DDoS Protection
Best for: Application and API flood mitigation without manual tuning
Strengths: Adaptive Threat Engine, edge mitigation, no attack-traffic fees
Things to consider: Advanced configuration and support responsiveness draw complaints
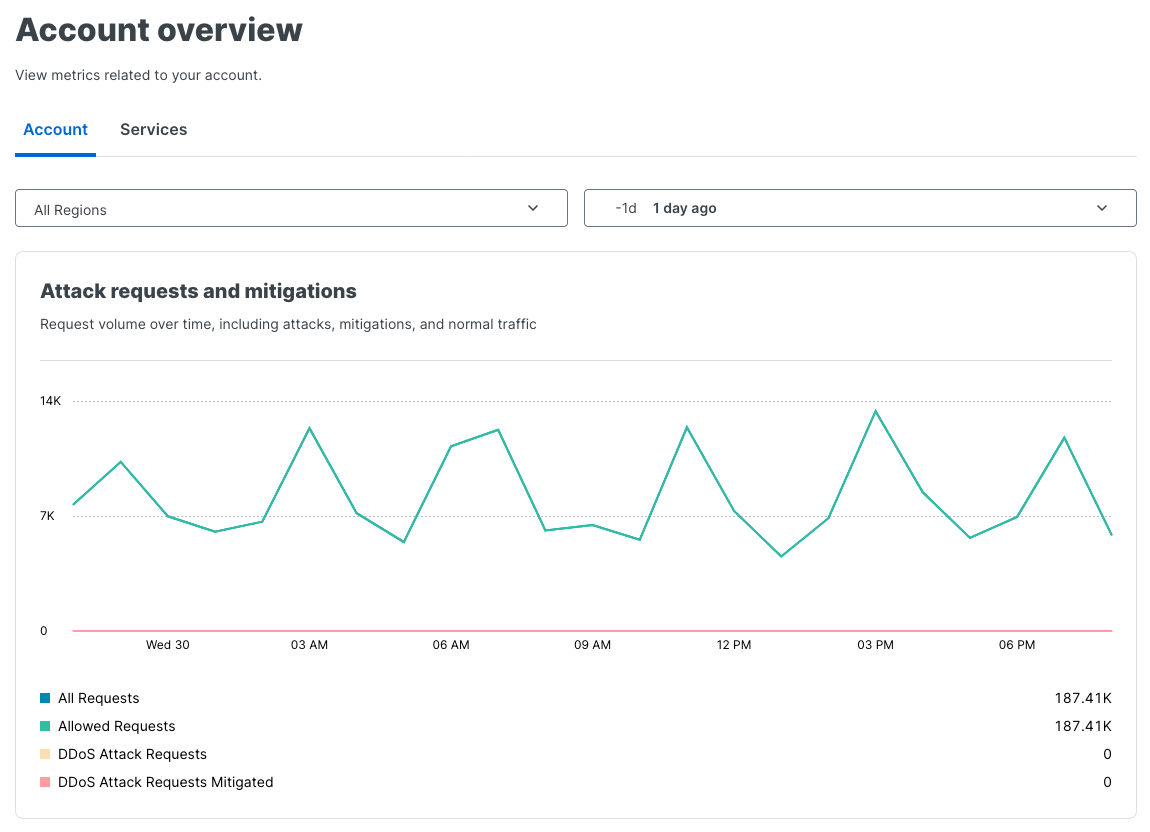
Fastly DDoS Protection builds mitigation rules automatically rather than relying on static rule sets. Its Adaptive Threat Engine validates whether an unexpected traffic spike is legitimate, and if it is not, scans traffic characteristics to isolate the attack even when the source IPs rotate.
Detection and mitigation logic run at the network edge rather than in a centralized scrubbing center, and the service is enabled with a single toggle. It can be deployed through a DNS change or by integrating with the wider Fastly platform, without installing hardware.
Key features include:
- Adaptive Threat Engine: Continuously analyzes traffic patterns to distinguish flash crowds from malicious botnets, then generates and updates signatures in near real time.
- Automatic rule generation: Tailored rules are built for each attack, so mitigation adapts as the attack changes without manual tuning.
- Edge network capacity: A global network offering 578 Tbps as of March 31, 2026, used to absorb network-layer floods while dropping non-HTTP and HTTPS traffic that is not relevant.
- Dynamic detection: Traffic and its attributes are watched continuously for anomalous deviations, regardless of the size of the organization.
- Near real-time mitigation: Attacks are blocked within seconds, and multiple synchronized attacks can be mitigated at once.
- Decipher DDoS visibility: Exposes every rule crafted during an attack so teams can check what was blocked and why.
- Billing on legitimate traffic: Charges are based on legitimate traffic only, so volumetric attack spikes do not incur delivery and egress fees.
- Platform-agnostic deployment: Works with on-premises, cloud, or hybrid environments via a DNS change or edge platform integration.
Limitations (as reported by users on G2, covering Fastly's wider web application and API security offering):
- Support responsiveness: Multiple reviewers report slow response times and difficulty getting help with configuration refinements.
- Licensing cost: Users describe pricing as high compared with alternative products, with additional charges when complex configuration changes need vendor assistance.
- Configuration effort: Reviewers report that defining rules is challenging and that setup and rule navigation can be time-consuming.
- Documentation: Several users note that available documentation and tutorials make it harder to use the full feature set.
- Traffic monitoring consistency: One reviewer reports data inconsistency issues when monitoring traffic.
Source: Fastly
7. AWS Shield
Best for: Protecting internet-facing workloads hosted on AWS
Strengths: Inline L3/4/7 mitigation, traffic baselining, response team
Things to consider: Key diagnostics and cost protection need the Advanced tier
AWS Shield protects networks and applications by identifying network security configuration issues and defending applications against active flood events. It is split into two capabilities: a network security director in preview that analyzes resources and surfaces configuration problems, and Shield Advanced, which delivers managed DDoS protection.
Shield Advanced provides automatic inline mitigation across layers 3, 4, and 7, drawing on AWS global threat intelligence. It baselines normal application traffic so anomalies can be detected as the application encounters threats such as HTTP floods and DNS query floods.
Key features include:
- Automatic inline mitigation: Shield Advanced detects and blocks flood events across layers 3, 4, and 7 without manual intervention.
- Traffic baselining: The service establishes a baseline of normal application traffic, then flags deviations, so defense adapts to each application's behavior.
- Layer-specific scrubbing: Protects applications and APIs from SYN floods, UDP floods, and other reflection attacks.
- Packet filtering and traffic shaping: Inline mitigations including deterministic packet filtering and priority-based traffic shaping stop basic network-layer attacks while limiting added latency.
- Shield Response Team: Provides expert guidance during active DDoS incidents, and customers can apply application-specific security controls.
- Network security director (preview): Assesses AWS resources and configurations, visualizes network topology, and prioritizes misconfigured or overlooked resources across accounts.
- Remediation recommendations (preview): Suggests services and rule sets for each configuration issue, with Amazon Q Developer available for natural language queries about network security posture.
Limitations (as reported by users on G2):
- Tier gating: Reviewers note that detailed attack diagnostics, proactive engagement, and cost protection require Shield Advanced, which is hard to justify for organizations needing only basic protection.
- Cost: Pricing is the most frequently raised concern, with several users describing the service as expensive.
- Billing clarity: One reviewer reports that some functions interfere with other services, making billing confusing.
- False positives: A user reports occasional false positives despite otherwise stable operation.
- Control granularity: Reviewers mention limited options for coordinating specific protections or triggering them at a chosen time, and requests for broader attack coverage in one place.
- Notification detail: One reviewer suggests attack notifications could include more detail.
8. Azure DDoS Protection
Best for: Azure virtual networks needing always-on network-layer defense
Strengths: Adaptive tuning, edge scrubbing, 15-minute rapid response SLA
Things to consider: Layer 7 needs a separate WAF, and pricing is often flagged
Azure DDoS Protection applies always-on monitoring and automatic mitigation to resources in Azure virtual networks. Traffic is scrubbed at the network edge before it reaches applications, and adaptive tuning compares observed traffic against thresholds defined in the DDoS policy so the service adjusts to each workload.
It covers network layer (layer 3 and 4) attacks and common application layer attacks, and interoperates with Azure Monitor, Microsoft Defender for Cloud, and Microsoft Sentinel. Two service options, Network Protection and IP Protection, cover different scopes of deployment.
Key features include:
- Adaptive tuning: Application traffic patterns are monitored for anomalies, with actual traffic compared against the thresholds set in the DDoS policy.
- Edge scrubbing capacity: Mitigation capacity absorbs and cleans flood traffic at the network edge before it reaches applications.
- Multilayer coverage: Defends against a comprehensive set of network layer (layer 3 and 4) attacks, plus common application layer (layer 7) attacks when paired with a web application firewall.
- Attack telemetry: Full visibility into attacks with actionable insights, logging, and alerting, with metrics appearing in the portal within about five minutes.
- Rapid response team: A DDoS Protection rapid response team available for investigation, custom mitigation, and analysis under a 15-minute SLA.
- Cost containment: Helps reduce DDoS-related usage spikes such as application scaling charges and bandwidth surges.
- Two service tiers: Network Protection and IP Protection cover different scales of deployment.
- Zone resilience: The service is zone-resilient by default and managed by the service itself, with no customer configuration required.
- Native integrations: Works with Azure Monitor, Microsoft Defender for Cloud, Microsoft Sentinel, and the wider Microsoft security suite.
Limitations (as reported by users on G2):
- Cost: Pricing is the most common criticism, with reviewers citing monthly costs that are hard to justify when the built-in platform protection is sufficient.
- Configuration control: One reviewer notes the inability to configure how different types of flood traffic are handled across requests.
- Missing controls: A user reports the absence of a mode to temporarily block all traffic during a sustained attack.
- Interface detail: Reviewers ask for a more detailed and user-friendly interface, and more visibility into mitigation details.
- Licensing and resource use: One reviewer mentions per-solution licensing and high processing resource consumption.
- Plan flexibility: A user would prefer the ability to apply different protection plans to different resources.
まとめ
Maintaining availability in the face of sophisticated traffic floods requires a proactive and multi-layered defense strategy. By combining real-time detection with automated mitigation at the network edge and application layers, organizations can protect their digital infrastructure from downtime. Continuous monitoring and adaptive tuning are essential to stay ahead of evolving threats and ensure long-term resilience.